 Success Story
Extending SailPoint & IGA
Close the gaps your IGA platform leaves.
learn more
Recommended reading
Success Story
 Blog
Identity data quality: the problem nobody wants to own.
Connecting an application moves the data. It does not make the data trustworthy. Blog
When a health system acquires another hospital, identity governance is the first casualty.
The deal closes in a boardroom. The governance gap opens on day one, and it does not close on its own.Featured
Success Story
EHR access, automated down to the template.
An academic medical center built its own role-based access layer for its electronic health record system with READI, avoiding a license increase of about $100,000 and handling data its IGA…
All content
Blog
Identity data quality: the problem nobody wants to own.
Connecting an application moves the data. It does not make the data trustworthy.
Blog
When a health system acquires another hospital, identity governance is the first casualty.
The deal closes in a boardroom. The governance gap opens on day one, and it does not close on its own. Blog
The hidden cost of “good enough” governance.
Manual workarounds produce the paperwork of governance without the control. The bill comes later. Blog
What “connected” actually means in identity governance (and why most integrations fall short)
A read-only connection tells you what access exists. Governance requires the ability to change it. Blog
Identity governance in healthcare: the clinical application blind spot.
The systems most likely to create risk are the ones your identity program cannot see. Blog
Identiverse 2026: identity governance’s unfinished business.
Identiverse 2026 Recap: Identity Is Still Cool, and the Problems Are Still Real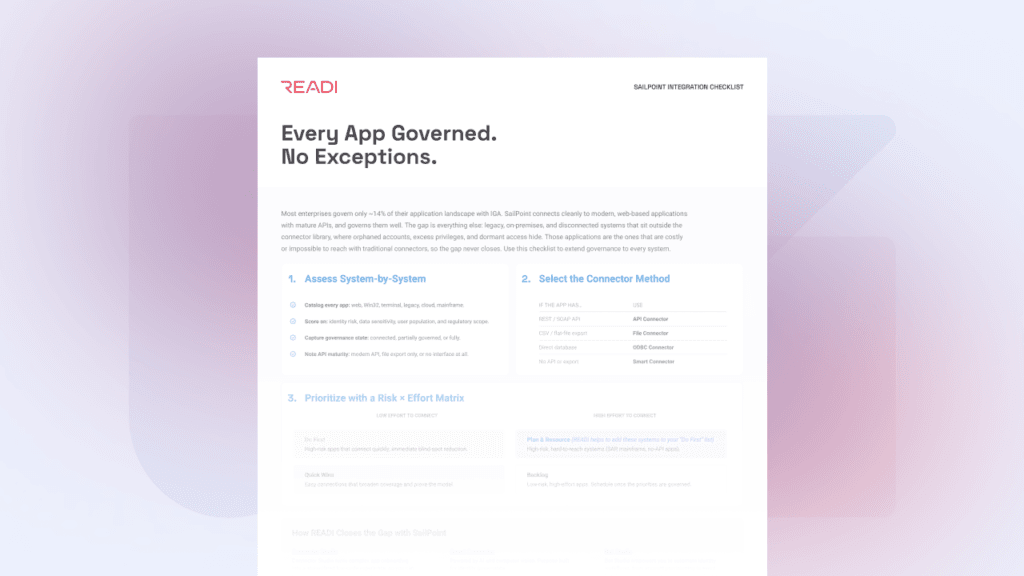 One Pager
SailPoint Integration Checklist
How to extend SailPoint governance to 100% of your applications, including a system-by-system assessment framework, connector method selection guide, and prioritization matrix. Blog
KuppingerCole 2026 revealed the IGA connector gap no vendor has closed.
KuppingerCole published its 2026 IGA Leadership Compass in May. It evaluated 31 vendors. It named Overall Leaders. It ranked platforms on product depth, innovation, and market presence. It is the… Blog
More connectors won’t fix your governance gaps.
If you have been evaluating identity governance solutions, you have probably seen the pitch: "We have 500+ connectors." Or 800. Or 1,200. The number keeps climbing, and the implication is… Solution Overview
READI+SailPoint
The disconnected application problem is not a catalog problem. It is a platform problem. READI gives your team the ability to build any connector fast, extending SailPoint Identity Security Cloud… Blog
Why partners are rethinking identity governance – and paying attention to READI
Most enterprises already own an Identity Governance and Administration (IGA) platform. Webinar
Why application onboarding is the real bottleneck in identity governance.
Disconnected, legacy, and homegrown applications create an invisible ceiling on identity governance. Most enterprises govern only ~14% of their application estate, leaving the majority outside policy, audit, and automati... Blog
Why generic RPA falls short for identity governance.
There’s a pattern I keep seeing. An enterprise rolls out an IGA platform. They connect the “big four” applications. Then they hit the long tail. Legacy systems. Vertical SaaS. Custom… Blog
Why identity governance fails at the application layer.
Identity governance has never been more important, or more challenging. Organizations continue to invest heavily in Identity Governance and Administration (IGA) platforms, modern access review programs, and lifecycle aut... Blog
From the Stage to the Booth: Thoughts on SailPoint Navigate 2025
Well, that's a wrap. Navigate 2025 (Austin version) has come to a close. I have a few reflections.IGA extension
Extend SailPoint governance without replacing your IGA.
Extending SailPoint governance means adding connectivity, data quality, and automation around SailPoint Identity Security Cloud or IdentityIQ so it can govern applications it cannot reach natively, without replacing it. The goal is to get more value from the IGA investment you have already made.
Where SailPoint governance gaps come from.
SailPoint governs well where applications connect through native connectors, APIs, and standard protocols. Every enterprise also runs legacy, on-premises, and custom applications outside that catalog. Certifications, policy enforcement, and offboarding stop at that boundary, and a longer connector list rarely reaches the systems that matter most. Native connectors cover the core of the portfolio. The long tail needs a different approach.
IdentityIQ modernization can open new gaps.
Teams moving from IdentityIQ to Identity Security Cloud often carry years of customization, including bespoke connectors, BeanShell rules, and complex workflows. These do not translate directly to a configuration-driven cloud model, so applications that relied on custom IdentityIQ connectors can lose coverage during the move. Planning for connectivity continuity early keeps modernization from creating new blind spots.
How READI extends SailPoint.
READI is a certified SailPoint Technology Partner and works alongside SailPoint, not in place of it. It connects the applications SailPoint cannot reach, cleanses and normalizes identity data before it arrives, and carries out SailPoint decisions such as certifications and terminations in those applications.
Start with the SailPoint Integration Checklist to assess and prioritize your application landscape. For a real example, see how an academic medical center built its own role-based access layer for an EHR system that its IGA platform could not handle. The resources on this page also cover connector strategy, identity data quality, and closing IGA gaps.
ten minutes, no sales call.